A JWK is the representation of signing and encryption in JSON format. JWKS is simply a set of cryptographic and signing keys expressed in JSON.
It is essential that the partner building the SSO expose a JWKS endpoint with public keys directly to us, so that we can verify the validity and integrity of the information our server will receive.
A JWK comes in linked pairs of public key and private key and usually has the following structure:
{
    "keys": [
        {
            "kty": "RSA",
            "e": "AQAB",
            "use": "sig",
            "kid": "m9L0aPfdtgdUCB0y2i2JN-oYcETaI4mQ93j0DwZ-K8Q",
            "alg": "RS256",
            "n": "psApL_i1m7CuwDiSB73H1fnXHn0mv3nz5dh1Qwl-GvWiHUfJICkAqm0hUQ36I6KH7z5NeTBzytJ8bdFPIWNfJt0cmcHApsPuE55E8vzi8_qkLGHJy52at_3w1dOyt0Ht4Ws0Lpitc6lNkwAKnYNxC8EKSPJMJL2W7H-c6PMi0bnyGEwTacm3sm8OJ00G5rWptWxFv2gPixn0ncyYhgqBSwWHUTbQ2-kAy5U3UTTPHqCyLUNJHjZaSx_ftQHPCCM8HHpFdC404DcVJTscs28vVbTZ8F4suICNUvIZex1WkIRw_p1xFnjRrScpaC-berdnAgmX80-zFP9KWnkidb_3Pw"
        }
    ]
}
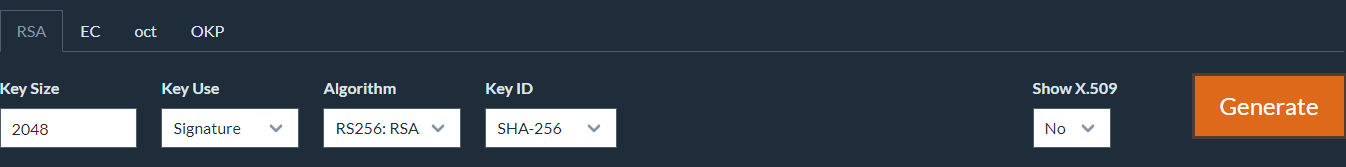
You can generate JWKs at https://mkjwk.org/ with the following configuration.